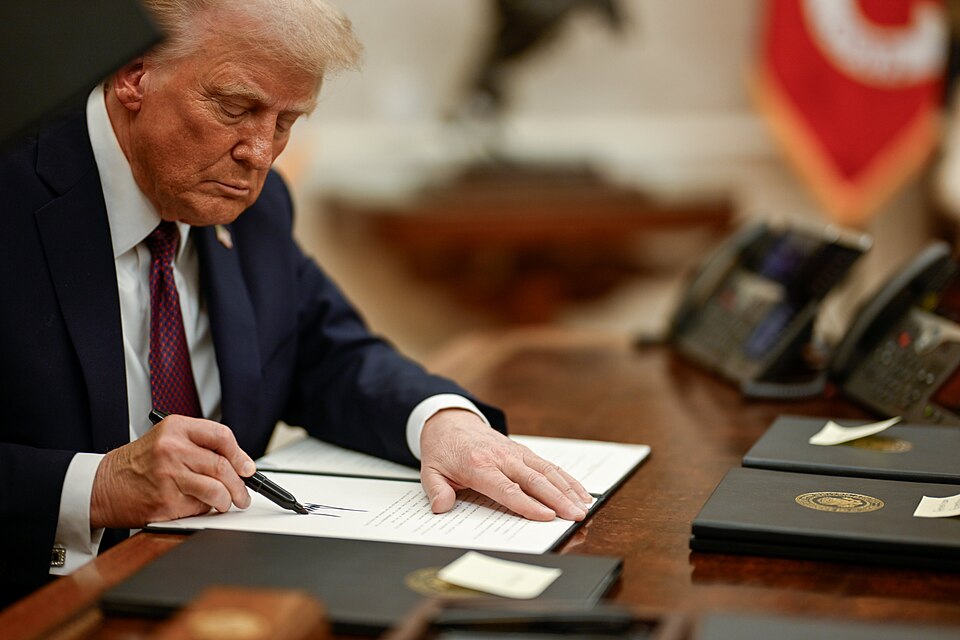
A newly signed White House memorandum, thin on public details, aims to give private businesses the legal ability to conduct offensive cyber operations against certain foreign actors, according to NPR — a significant shift in US cyber policy that would effectively deputize private industry into activities historically reserved for the NSA, US Cyber Command, and other government agencies. The ‘hack-back’ concept has been debated in cybersecurity policy circles for years; this memo appears to formalize elements of it in executive action for the first time.
2-MINUTE CONTEXT — WHAT “HACK BACK” MEANS
‘Hack back’ refers to the concept of allowing individuals or organizations that have been the victims of a cyberattack to conduct retaliatory offensive cyber operations against the attacker. The specific activities that ‘hacking back’ might include: accessing the attacker’s systems without authorization; disrupting or degrading the attacker’s infrastructure; exfiltrating data from the attacker; or destroying files or systems that the attacker is using.
Currently, all of these activities are illegal under the Computer Fraud and Abuse Act (CFAA) regardless of whether the target initiated the attack. The CFAA does not have a self-defense exception for cyber operations. A private company that has been hacked by a foreign nation-state cannot legally access the attacker’s systems even to retrieve its own data or stop an ongoing attack. The White House memo appears to create a legal pathway that modifies this constraint for certain foreign actor scenarios.
WHY THE CYBERSECURITY COMMUNITY IS CONCERNED
The cybersecurity policy community has been debating hack-back for years, and the consensus among most experts is negative. The specific concerns:
▸ Attribution is hard: private companies cannot reliably determine who is actually attacking them; a company that thinks it is hacking back against a Russian intelligence operation may actually be disrupting a hospital in Germany whose systems the Russian hackers are using as a relay
▸ Escalation risk: offensive cyber operations against foreign actors, even retaliatory ones, can escalate into broader cyber conflicts; private companies do not have the intelligence context to assess escalation risk the way government cyber operators do
▸ Friendly fire: the infrastructure that foreign hackers use to conduct attacks frequently runs through or includes legitimate systems in neutral or allied countries; hack-back can damage those systems
▸ Norm erosion: if US private companies can hack foreign actors, other countries’ private actors have a precedent for hacking US companies; the norm against private offensive cyber operations protects the US as much as it constrains it
▸ Legal jurisdiction: US private companies conducting offensive operations against systems in other countries may violate those countries’ laws, creating international legal exposure
The problem with hack-back is not that victims don’t deserve to defend themselves. It is that private companies cannot do it without hitting things they didn’t intend to hit, because they don’t know the full map.
WHAT THE MEMO ACTUALLY DOES — AND WHAT WE DON’T KNOW
The memo is described as ‘thin on public details,’ which means ONYX cannot definitively characterize what it authorizes, what constraints it imposes, what oversight mechanisms it establishes, or which specific foreign actors it targets. The broad framing is that private businesses can conduct offensive operations against ‘certain foreign actors.’ The specific limiting conditions — which foreign actors? What operations? What authorization process? What reporting requirements? — are not yet public.
ONYX covers the memo at the level of confirmed reporting. The fact that the memo exists and broadly authorizes private offensive cyber operations is from NPR. The specific implementation details require the memo itself, which has not been published.
THE SPR PARALLEL — CONTEXT FROM THE SAME WEEK
The hack-back memo arrives the same week the US Strategic Petroleum Reserve fell below 300 million barrels for the first time since the 1980s — a data point that reflects the Iran war’s accumulated economic costs. Both developments reflect the same underlying dynamic: the Iran war has produced sustained pressure on US government resources (energy reserves, military stockpiles, deployed assets) that is producing new policy responses. The hack-back memo may be partly a response to the documented increase in foreign cyberattacks on US infrastructure during the Iran war period — including the Minnesota water system attacks (ONYX August 12 coverage).
WHAT HAPPENS NEXT
▸ Full memo text — if and when published, will reveal the specific constraints and authorization process
▸ Congressional oversight — members of the Intelligence and Armed Services committees will request briefings on the memo’s implementation
▸ Cybersecurity industry response — private sector cybersecurity companies will assess whether the memo’s protections are sufficient to actually justify offensive operations
▸ International reaction — foreign governments will assess whether this memo changes US cyber posture in ways that affect their own policies
▸ Test case — the first documented private company offensive operation under the memo’s authority will be the practical test of whether its constraints work
| CONFIDENCE: MODERATE | White House hack-back memo existence and broad authorization framing are from NPR confirmed reporting. Specific implementation details are not yet public. CFAA legal context is from established law. Cybersecurity community concerns analysis is ONYX editorial based on established cybersecurity policy literature. |
| ⚖️ BIAS CHECK — WHO IS SAYING WHAT | |
| Trump Administration | Framing as protecting American businesses from foreign attack; thin on public detail suggests sensitivity about the scope |
| Cybersecurity Industry | Divided: some private sector security firms have long advocated for hack-back authority; most cybersecurity policy experts are skeptical |
| NSA / US Cyber Command | Will have operational concerns about private sector actors operating in their domain without their intelligence support |
| Foreign Governments (Russia, China, Iran, North Korea) | The primary targets of hack-back authority; will likely characterize any private offensive operations as acts of war or state-sponsored aggression |
| Congressional Oversight Committees | Will seek the full memo text and implementation guidance; both parties have cybersecurity oversight interests |
SOURCES
▸ NPR — White House hack-back memo, August 2026
▸ Computer Fraud and Abuse Act — established law on unauthorized computer access
Q: Is this legal under international law?
A: International law on offensive cyber operations is underdeveloped. The Tallinn Manual (a non-binding academic assessment of how international law applies to cyber) suggests that state-sponsored or state-authorized offensive cyber operations can constitute acts of war under some circumstances. Whether private company operations authorized by a government memo constitute state action under international law is genuinely contested.
Q: Why hasn’t hack-back been authorized before?
A: The CFAA has historically been interpreted to prohibit all unauthorized computer access regardless of intent. Multiple proposals to create a hack-back exception have been introduced in Congress and not passed, primarily due to the attribution, escalation, and friendly-fire concerns described in this article. The White House memo appears to bypass the Congressional route by using executive authority.